Application Modernization and Operational Resilience in Financial Services
Six modernization approaches for financial services applications, the resilience risks they carry, and suggested acceptance criteria for regulated firms.
 admin
Six modernization approaches for financial services applications, the resilience risks they carry, and suggested acceptance criteria for regulated firms.
Most enterprise network changes are still made by hand. A firewall-rule automation case study and six steps for teams starting network automation.
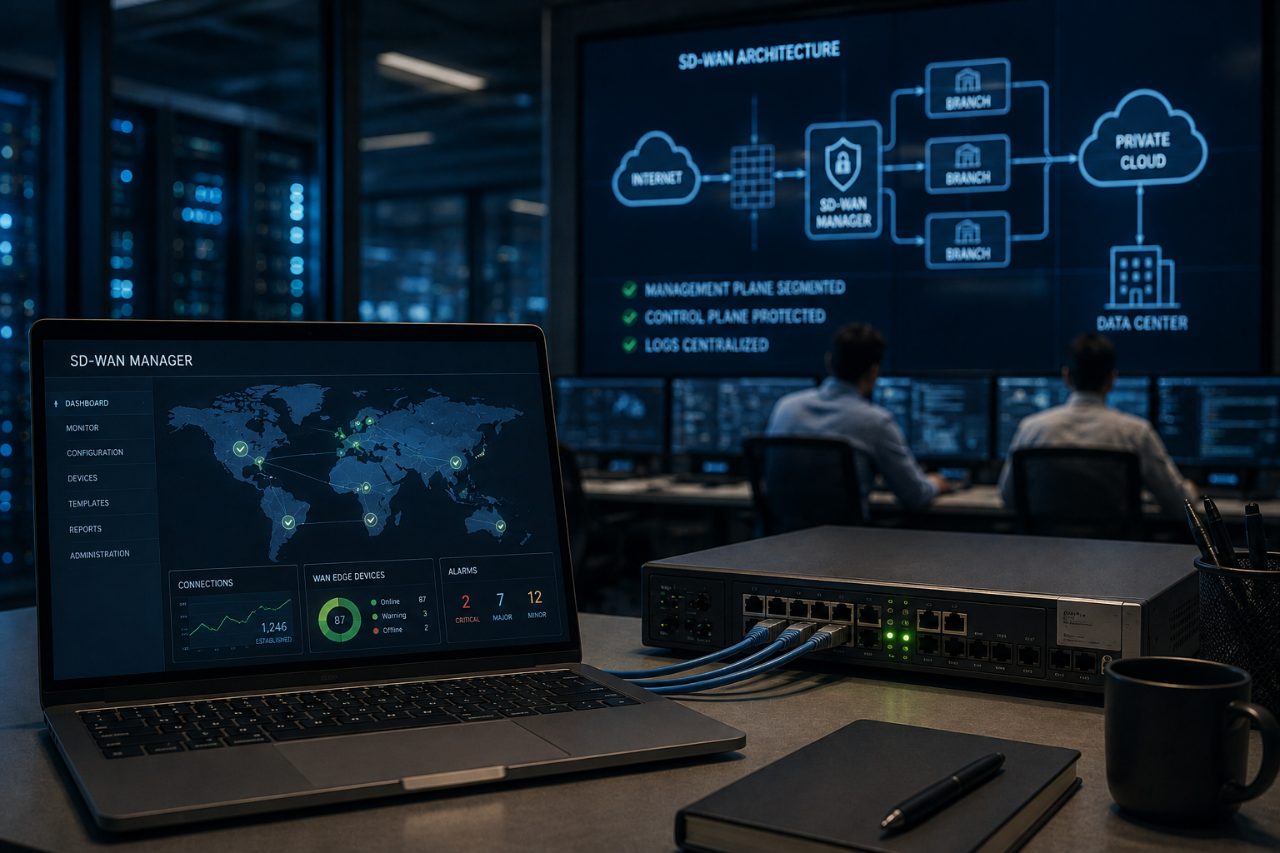
Upgrading to a fixed software release closes a vulnerability, but the design decision that put the vulnerable system within reach of the internet stays open until the network is redesigned to close it. That distinction is the lesson running through 2026’s sustained campaign against Cisco Catalyst SD-WAN, and it bears directly on the work Ahead does for … Read more
The network team and the incident response team have rarely reported to the same person. Gartner’s Predicts 2026: Cybersecurity Program Rebrands to Cyber Resilience expects that to change: by 2028, half of CISOs will be asked to own disaster recovery on top of incident response. For the finance and insurance firms Ahead works with in Japan, … Read more
Ahead has written before about the shortage of engineers who can maintain Japan’s aging COBOL and mainframe systems, a gap opening as experienced people retire faster than they can be replaced. A second gap is now forming at the opposite end of the career ladder, and it has the same long-term shape: if firms stop hiring and … Read more
Japan’s core banking and insurance systems still run on COBOL and mainframes, and the engineers who understand them are retiring faster than replacements arrive. Japan’s Ministry of Economy, Trade and Industry (METI) named this problem years ago, the “2025 Digital Cliff,” warning that continued legacy dependency could cost the economy as much as 12 trillion yen a … Read more
While quantum decryption capable of breaking today’s encryption is still likely years away, the data being protected by that encryption isn’t going anywhere. Encrypted traffic captured and stored now can simply be revisited later once the capability catches up. So the real question for regulated organizations isn’t when this becomes possible, but whether today’s cryptography … Read more
AI tooling is being adopted faster than the policies around it, and two patterns keep showing up. The first is uneven access. Engineering teams working in regulated or security-sensitive environments are often the most restricted: tool approvals take months, data classification requirements are strict, and budget sign-off adds another gate. Meanwhile, AI access sometimes appears … Read more
AI is entering infrastructure work fast, but it does not land evenly across the stack. The first impact shows up in repeatable operational workflows and high-volume text work. The slower impact shows up where delivery is constrained by real enterprise conditions: regulated environments, multi-vendor dependencies, change windows, and accountable outcomes. In Ahead’s work, most of … Read more
Infrastructure system patch cycles expose a useful truth: technical change is rarely the hardest part. In large environments, risk comes from how change is governed across teams, systems, and constraints. The same pattern shows up in higher-impact work such as network migrations, firewall policy redesign, identity changes, platform upgrades, and infrastructure transitions. The work is … Read more