Upgrading to a fixed software release closes a vulnerability, but the design decision that put the vulnerable system within reach of the internet stays open until the network is redesigned to close it. That distinction is the lesson running through 2026’s sustained campaign against Cisco Catalyst SD-WAN, and it bears directly on the work Ahead does for finance and insurance clients in Japan: designing and segmenting the networks these SD-WAN management systems sit inside.
1. The target is the management plane
Through 2026, Cisco disclosed a run of Catalyst SD-WAN vulnerabilities that CISA confirmed as actively exploited and added to its Known Exploited Vulnerabilities catalog, including two maximum-severity, CVSS 10.0 authentication bypasses. Cisco’s own Talos threat intelligence team attributes much of this to a single sophisticated actor it tracks as UAT-8616, with evidence of exploitation going back to 2023. The pattern reveals a single objective rather than a scatter of unrelated bugs: repeated attempts to reach the same place, the SD-WAN Manager and Controller, the central consoles that configure and orchestrate the entire network fabric. Talos documented the playbook, which is bypass authentication to land on an internet-facing Manager or Controller, escalate to root, then establish persistence through injected SSH keys, NETCONF configuration changes, and log clearing.
Why that target? Leverage. An attacker who compromises a branch router controls one site, whereas one who reaches the Manager can push configuration out to every device on the network at once. That central control also makes the console expensive to take offline, since rebooting or reimaging it disrupts the entire network, which is why attackers prize it and defenders hesitate to touch it under pressure.
2. The official guidance is an architecture instruction, not a software update
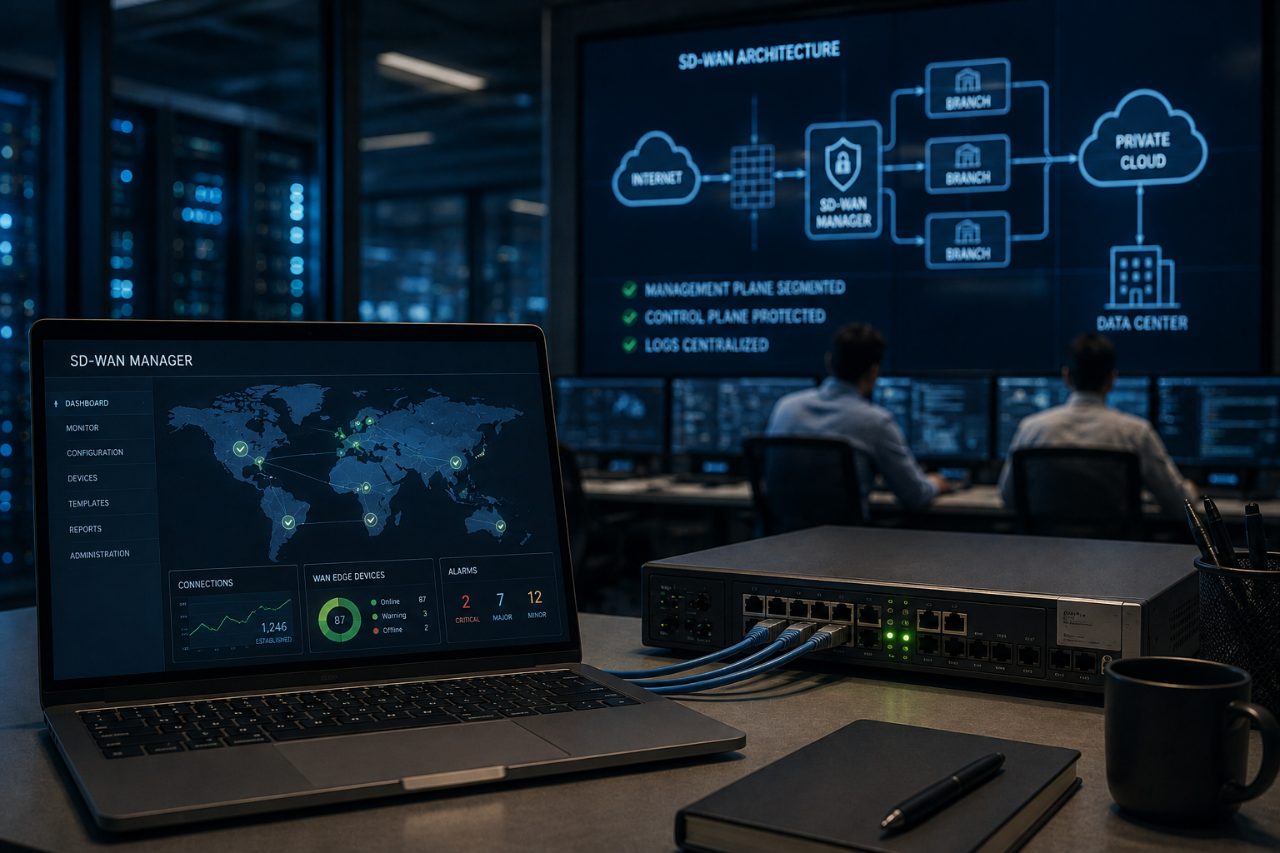
The most important line in the government response concerns architecture rather than patching. CISA issued Emergency Directive 26-03, and Five Eyes agencies, including Australia’s ACSC, published a joint hunt guide with a blunt central mandate: management interfaces must never be exposed to the internet, and control components must sit behind a firewall. Systems with exposed management interfaces were the primary targets and at the highest risk of full compromise. Cisco reinforces the point, noting that for the critical authentication-bypass flaws there are no workarounds that fully fix the vulnerability. Whether the management plane was reachable from an untrusted network was a design decision made long before any CVE was published, and it is the single factor that most determined which organizations were exposed.
3. The software upgrade alone does not settle it
The UAT-8616 tradecraft makes the limits of a software upgrade concrete. Talos and intelligence partners describe the actor downgrading a Controller to an older vulnerable version, exploiting a legacy 2022 flaw to reach root, then restoring the current version to hide the path. An administrator checking the running version would see the correct, fixed build while root-level persistence remained in place. Cisco’s remediation guidance reflects this, advising customers to preserve forensic evidence before upgrading, rotate credentials and secrets held in device configurations, and review trusted SSH keys and configuration templates. In other words, on a management plane, “we upgraded to the fixed release” and “we have confirmed the device was not already compromised” are two separate claims, and the software upgrade settles only the first.
4. What this means for network design in regulated environments
For finance and insurance firms running SD-WAN across branch networks, three design decisions carry more weight than the speed of the next upgrade. The first is reachability. If the management plane can be reached from anything beyond a tightly controlled administrative network, that is the exposure to close first, because internet reachability is what separated the compromised from the safe in this campaign, regardless of how current the software was. The second is segmentation. Control components sitting behind a firewall, as the Five Eyes guidance requires, mean a foothold on one service stops there instead of opening a path to the rest of the network, which is the difference between an incident and a breach. The third is logging. Because the actor cleared local logs to frustrate investigators, logs have to be shipped off the appliance to a protected store before an intrusion happens, since a firm relying on on-box logging alone would lose the evidence at the same moment it most needs it.
Where Ahead fits
This is network design work rather than a software update, and it is what Ahead Group does for finance and insurance clients in Japan. That means placing SD-WAN management and control components behind proper segmentation rather than within reach of untrusted networks, forwarding logs off the appliance so an intrusion cannot be erased locally, and designing the network so that a single compromised console stays contained instead of surrendering the entire network. If you are running SD-WAN across multiple sites and want the architecture reviewed against how these systems are actually being attacked, learn more about our Managed Services.